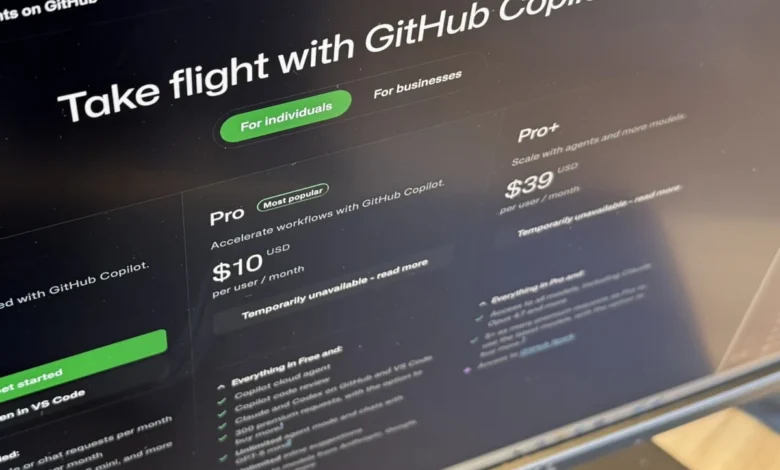
GitHub’s latest evolution of its Copilot ecosystem marks a definitive shift from simple code-completion assistance to an orchestration-heavy, agentic development environment. Unveiled at the annual GitHub Universe conference, these enhancements represent the company’s aggressive strategy to move beyond the "autocomplete" era and into an age where autonomous agents manage the lifecycle of complex software projects. By integrating a redesigned central application with the new Copilot Projects feature, GitHub aims to consolidate the fragmented toolchains that have historically defined enterprise software development.
The Evolution of GitHub Copilot
Since its inception, GitHub Copilot has evolved rapidly. In 2021, the tool debuted as a technical preview, focusing primarily on ghost-text suggestions within IDEs. By 2023, GitHub began integrating chat interfaces and CLI support. The 2026 updates represent the third major wave of this trajectory: the transition from "assistant" to "agent."
The new architecture moves the developer experience out of the siloed IDE and into a centralized, context-aware workspace. This workspace acts as a mission control center where agents do not merely suggest code; they interpret specifications, parse design documentation, digest Slack communication, and monitor application telemetry. By allowing these agents to access the broader "context" of a business—not just the raw code—GitHub is positioning itself as the operating system for the AI-augmented software development life cycle.
Copilot Projects: Orchestrating the Autonomous Workforce
At the heart of this update is Copilot Projects, a feature designed to solve the "multi-agent coordination problem." In traditional enterprise settings, developers spend significant portions of their day manually managing dependencies, context-switching between Jira, GitHub, and documentation, and ensuring that individual pull requests align with organizational goals.
Copilot Projects changes this dynamic by allowing a human lead to define high-level goals. Once an objective is set—such as "migrate all legacy Java services to the latest framework version"—the system decomposes that goal into discrete tasks. These tasks are then distributed across multiple agents that work in parallel across disparate repositories.
This parallel processing capability is particularly vital for large-scale technical debt reduction. Whether it is updating deprecated SDKs, addressing widespread API deprecations, or refactoring shared libraries, the system can execute these tasks concurrently, submitting individual pull requests for human review. This shifts the developer’s role from a "code writer" to an "architect and validator," where the primary responsibility becomes defining the intent and verifying the output of the machine-generated work.
Strategic Implications for the Enterprise
For Chief Information Officers (CIOs) and engineering leads, the move toward a unified, agentic platform offers both a boon and a significant governance challenge. Analysts at firms like Avasant and Pareekh Consulting have noted that the primary advantage for enterprises is the reduction of "tool sprawl." By standardizing AI-assisted development on the GitHub platform, leadership can enforce consistent security policies, audit trails, and governance frameworks across thousands of developers.
However, this centralization requires a new approach to security. Amit Kumar Jena, AI development head at Kanerika, emphasizes that "the ability of agents to independently commit code necessitates a zero-trust model for AI." Enterprises are advised to implement strict repository-level access controls, enforce mandatory branch protection, and integrate audit logs directly into their Security Information and Event Management (SIEM) systems. Without these safeguards, the scale afforded by autonomous agents could inadvertently introduce vulnerabilities faster than human teams can detect them.
The Coordination Paradox: Challenges of Multi-Agent Systems
While the theoretical gains in productivity are substantial, industry analysts warn of a "coordination paradox." As more agents are deployed simultaneously, the risk of technical conflict rises. If Agent A updates a library version while Agent B is refactoring a component that relies on that specific library, integration conflicts are inevitable.
Furthermore, a 2026 study published on arXiv, CooperBench: Why Coding Agents Cannot Be Your Teammates Yet, provides a cautionary backdrop for this rollout. The study found that while individual agents performed well, their success rates dropped by approximately 30% when forced to collaborate on shared tasks. This indicates that without robust conflict-resolution protocols, enterprises could face a surge in merge conflicts and broken CI/CD pipelines.
To mitigate this, GitHub has introduced the "Max" tier of its code review functionality. Unlike previous iterations that used a single model to scan for bugs, the Max tier employs a multi-model ensemble approach. Several independent AI reviewers analyze the code, and an "aggregation agent" reconciles their findings, acting as a final arbiter before presenting a consolidated report to a human developer. This multi-layered approach is designed to catch security-sensitive flaws that a single model might overlook, though it significantly increases the computational cost of each review.
The Shift to Consumption-Based Economics
The introduction of the "Max" tier also highlights GitHub’s pivot to a consumption-based pricing model. By moving away from flat-rate seat licensing to an AI-credit system, GitHub is aligning its revenue model with the actual computational load of AI agents.
According to internal estimates, the cost structure is tiered:
- Lite Reviews: $0.25 per execution.
- Balanced Reviews: $1.50 per execution.
- Max Reviews: $10.00 per execution.
This tiered pricing forces CIOs to make strategic decisions regarding where to deploy the most "intelligent" agents. While the Max tier is ideal for critical security-sensitive code, it is economically inefficient for trivial refactors. The challenge for management will be setting guardrails—such as AI credit limits per project—to prevent runaway costs, especially in scenarios where agents engage in iterative, self-correcting loops that could burn through credits rapidly.
Looking Toward the Future
The integration of these features into GitHub Enterprise marks a pivotal moment in the industry’s adoption of Generative AI. By embedding agentic workflows directly into the tools where code is already managed, version-controlled, and deployed, GitHub is effectively removing the barrier to entry for AI-driven software engineering.
However, the transition remains a work in progress. As Abhishek Satapathy of Avasant notes, "The technology is moving faster than the governance." The ultimate success of these tools will depend not on the sophistication of the AI models themselves, but on how effectively organizations can integrate these systems into their existing human-centric review processes.
The next 12 to 24 months will serve as the proving ground for these technologies. As enterprises begin to replace manual workflows with autonomous agent pipelines, the focus will shift from "can the AI write the code?" to "how can we safely orchestrate a workforce of silicon-based contributors?" For developers, the future is clear: the ability to manage, prompt, and validate AI agents will become a core competency, potentially rivaling the importance of syntax proficiency in the years to come. GitHub’s roadmap suggests they are betting the entire platform on this premise, setting the stage for a fundamental restructuring of how software is built, audited, and shipped in the enterprise.
Related posts: