AI-Driven Cyber Attacks Surge Globally as Threat Actors Industrialize Autonomous Tools and Large Language Models

The landscape of international cybersecurity is undergoing a fundamental transformation as malicious actors increasingly embed artificial intelligence directly into offensive operations. Recent intelligence disclosed by prominent security researchers highlights an alarming escalation in AI-orchestrated and AI-assisted cyber attacks. Rather than serving merely as an experimental novelty, artificial intelligence has firmly established itself as an indispensable operational component for advanced persistent threat (APT) groups and cybercrime syndicates worldwide.
Recent investigations conducted by cybersecurity firms such as TrendAI, Microsoft, and Rapid7 reveal that threat actors are leveraging autonomous frameworks, large language models (LLMs), and custom agentic systems to accelerate reconnaissance, automate vulnerability validation, and industrialize social engineering. This integration has dramatically compressed the timeline of modern cyber assaults, reducing the window between the initial discovery of a software flaw and its large-scale weaponization to a matter of hours.
The Anatomy of AI-Driven Operations in East Asia
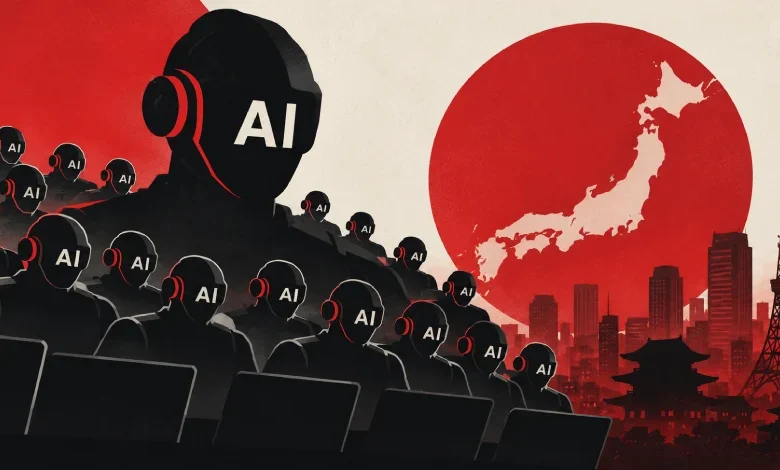
The scope of this technological shift was brought into sharp focus following the exposure of server environments used by malicious operators targeting organizations in Japan, South Korea, and neighboring regions. Security analysts examining these compromised staging grounds discovered comprehensive repositories of reconnaissance data, target lists, attack scripts, command histories, and automated reporting logs. These artifacts demonstrated a stark evolution from manual, ad-hoc hacking methodologies to highly structured, repeatable workflows driven by artificial intelligence.
In one notable campaign investigated by Trend Micro’s enterprise security division, threat actors deployed CyberStrikeAI—an open-source penetration testing tool—to conduct sweeping validation activities against at least 19 organizations in a remarkably brief timeframe. Concentrated largely in October 2026, this campaign utilized a network of 44 distinct AI agents to delegate tasks across the entire attack lifecycle. The automated platform handled everything from initial vulnerability discovery and validation to exploitation, command-and-control establishment, data exfiltration, and the generation of localized Japanese phishing pages and compliance-style reports.
Security experts noted that each targeted organization received a standardized report and an index of evidence generated automatically by the platform. This systematic output underscores how autonomous agents allow threat actors to scale their operations exponentially without requiring a proportional increase in human manpower.

A Chronology of Escalating AI Weaponization
The timeline of AI integration in offensive cyber operations has accelerated rapidly over recent years, shifting from theoretical concepts to widespread, active exploitation.
- Early to Mid-2026: Threat actors begin heavily weaponizing off-the-shelf and open-source penetration testing frameworks, such as ARTEX and CyberStrikeAI. These tools are increasingly integrated into automated password-spraying and reconnaissance scripts targeting cloud infrastructure and enterprise edge devices.
- August – September 2026: A specialized human-led campaign heavily assisted by large language models targets geographic information system (GIS) servers. Utilizing default credentials, attackers compromise sensitive cadastral records, commercial files, and enterprise credentials over a 24-day operational window. Concurrently, campaigns emerge targeting AI inference services to illegally acquire large-scale compute capacity at low cost.
- October 2026: State-aligned and financially motivated groups ramp up operations. Microsoft exposes the activities of the China-linked threat actor Storm-0940, which utilized the ARTEX framework to compromise a ConnectWise cloud backup application and rapidly sign into more than 2,250 Microsoft 365 tenants. South Korean authorities simultaneously announce the arrest of seven suspects linked to an industrial-scale extortion campaign utilizing AI-assisted tools to breach over 90 organizations, siphon 8.2 million records, and demand millions in ransom.
- Late 2026: Global threat reports from firms like Rapid7 and TrendAI confirm that generative AI has successfully shortened the median time from vulnerability discovery to weaponization to well below 24 hours. The underground market for commoditized offensive AI tools—including APEX AI, MessiahGPT, and DarkGPT—experiences a significant boom.
Diverse Use Cases: From Autonomous Agents to Script Generation
Security research reveals that artificial intelligence is being deployed across a spectrum of sophistication, categorized primarily into three distinct operational tiers.
At the highest level of autonomy are fully agentic platforms like those utilizing ARTEX or CyberStrikeAI. These systems manage entire attack chains independently, executing reconnaissance, testing network perimeters, and compiling structured reports with minimal human intervention.
The second tier involves human-led operations accelerated by large language models. In these scenarios, human operators utilize conversational AI and specialized LLMs to rapidly plan attack vectors, write custom exploit code, and optimize infrastructure deployment. Investigators tracking these campaigns observed intrusions targeting edge devices from prominent vendors—such as Cisco, Citrix, F5, and Yamaha—using publicly disclosed vulnerabilities and configuration file credentials. Furthermore, some of these operations have specifically targeted AI workflow platforms to hijack expensive inference capacity for unauthorized computational tasks.
The third, more foundational tier involves AI serving purely as a coding assistant. Threat actors employ models to refine scripts, debug malicious payloads, and automate routine administrative tasks. While less autonomous, this application still grants experienced operators a significant productivity boost, allowing them to execute multiple simultaneous campaigns against targets across the United Kingdom, France, Italy, Qatar, Colombia, and beyond.
Official Responses and Industry Warnings
Major cybersecurity entities and technology conglomerates have responded to these developments with urgent warnings regarding the changing threat landscape. Industry leaders emphasize that while artificial intelligence does not fundamentally alter the nature of system vulnerabilities—hackers are still exploiting unpatched software, weak passwords, and misconfigured access controls—it fundamentally changes the economics of cybercrime.

According to Microsoft’s comprehensive Digital Defense Report, the lowering barrier to entry has allowed less sophisticated actors to execute advanced, persistent attacks that were previously the exclusive domain of elite state-sponsored groups. The commercialization of underground AI tools—peddling stolen provider session tokens alongside specialized malicious software—has democratized access to sophisticated cyber weapons.
Law enforcement agencies are also stepping up international cooperation to combat the trend. Following investigations in South Korea, authorities dismantled a prominent cybercriminal cell that exploited AI-driven frameworks to target domestic businesses. Prosecutors revealed that the operation utilized automated penetration tools to breach dozens of entities, extracting millions of sensitive records and attempting to extort substantial sums in cryptocurrency. Officials stressed that the involvement of former cybersecurity professionals in developing and executing these automated schemes indicates a worrying trend of specialized talent migrating to the illicit economy.
Broader Implications and Future Outlook
The maturation of AI-driven cyber operations carries profound implications for global enterprise security and digital resilience. Security analysts point out that artificial intelligence acts simultaneously as a force multiplier for attacks and a significant expansion of the digital attack surface.
As automated agents continue to reduce the time, skill, and financial investment required to launch multi-stage cyber assaults, traditional signature-based defense mechanisms are increasingly insufficient. Organizations can no longer rely on human response speeds alone to mitigate threats that unfold at machine speed within minutes of a vulnerability disclosure.
In response, cybersecurity researchers and platform developers are racing to integrate defensive artificial intelligence into enterprise security architectures. Automated patch management, behavioral anomaly detection, and AI-driven threat hunting are becoming vital components of modern organizational defense strategies. However, experts caution that the ongoing arms race between attackers and defenders will continue to test the limits of digital infrastructure.
Ultimately, the widespread adoption of artificial intelligence by malicious actors signals the close of an era where cyber attacks were constrained primarily by human operational bandwidth. As APT groups and cybercriminals normalize the use of autonomous agents and LLMs, the imperative for organizations to adopt proactive, automated, and resilient security postures has never been more urgent.