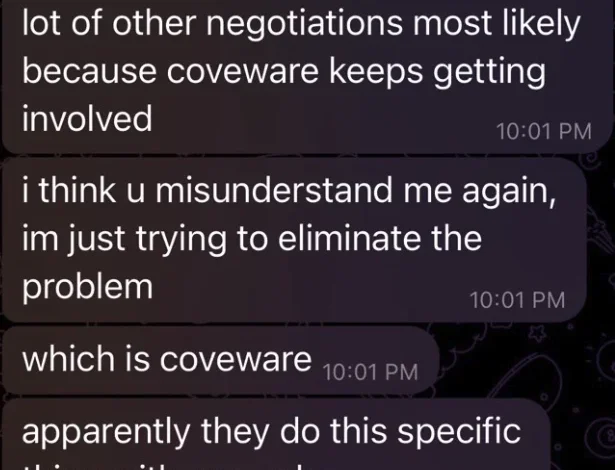
The ongoing federal investigation into the ShinyHunters group—a collective responsible for extorting more than $70 million from organizations this year alone—has taken a dramatic turn. Authorities have identified executives at two distinct ransomware negotiation firms who allegedly maintained collaborative relationships with the group, with at least one U.S.-based executive suspected of actively assisting in the operation of a victim-shaming portal used to pressure companies into paying ransoms. This development highlights a growing concern within the cybersecurity industry: the potential for systemic conflicts of interest and criminal complicity within the multi-billion dollar ransomware remediation market.
A History of Escalation: From France to Jordan
The ShinyHunters brand has been a persistent threat since its emergence in 2019. Initially, the group operated primarily out of France, orchestrating a wave of high-profile data breaches. As law enforcement agencies across Europe and North America tightened the net, arresting and incarcerating the group’s founding members, the leadership structure shifted. By the mid-2020s, the brand was consolidated under the control of a teenage hacker from Amman, Jordan, known by the alias "Rey."
Rey’s tenure at the helm marked a shift toward more aggressive tactics. The group transitioned from simple data theft to sophisticated, targeted extortion, culminating in the breach of the FBI’s recruitment portal, fbijobs.gov, in September 2026. By exfiltrating sensitive files—including medical records, psychological evaluations, and internal personnel data—the group signaled a willingness to target the highest levels of U.S. government infrastructure to amplify its leverage.

The Breakdown of the ShinyHunters Network
The FBI’s recent progress is largely attributed to the arrest of Dutch national Pepijn van der Stap on September 15, 2026. Dutch law enforcement executed a high-stakes operation, utilizing flash-bang grenades to apprehend Van der Stap while he was actively managing his digital accounts. The critical breakthrough occurred when investigators gained access to Van der Stap’s Signal messaging history.
These communications provided a roadmap of the group’s inner circle, including interactions with ransomware negotiators in Canada and the United States. Evidence suggests that Van der Stap’s digital trail also hinted at a more sinister layer of the group’s operations: a potential murder-for-hire plot, allegedly ordered by Van der Stap himself, though there is no evidence that these planned attacks were ever carried out.
The Arrest of Edward Dubrovsky
The investigation’s scope widened significantly on October 9, 2026, with the arrest of Edward Dubrovsky, a 54-year-old Canadian cybersecurity executive. Dubrovsky, who had previously authored a book advocating for engagement with ransomware actors, was charged with interfering with interstate commerce through extortion and threatening to disclose stolen data.
Court records, currently under seal, reflect the gravity of the allegations. Sources close to the investigation indicate that Van der Stap’s chat logs showed Dubrovsky possessed advance knowledge of the FBI data breach well before the hackers threatened to release the information publicly. Despite his role as a security professional, Dubrovsky reportedly failed to notify the bureau, raising critical questions about his professional obligations and potential alignment with the criminal enterprise.

The Rise and Fall of Shinywire
A pivotal piece of evidence in the government’s case is the website "shinywire[.]com," a now-defunct portal that functioned as a centralized hub for ShinyHunters to publish stolen data and demand payments. Active from May 2026 until mid-October, the site listed nearly 100 corporate victims.
Investigators believe that executives at a prestigious, large-scale U.S. consulting firm played an active role in maintaining this site. While the firm has not yet been named, its involvement suggests a degree of collaboration that goes beyond mere negotiation. The site served as a digital "shaming" blog, where victims were given a seven-day window to negotiate before their sensitive data was leaked on the Tor network. The inclusion of companies like Intuitive Surgical, which suffered a major breach earlier in 2026, illustrates the scale of the operation.
Conflicts of Interest: The "Pay-to-Play" Problem
The involvement of ransomware negotiators in criminal schemes is not entirely unprecedented, but the scope identified in the ShinyHunters case is uniquely alarming. Industry experts have long warned about the "success fee" model employed by some remediation firms. In this structure, negotiators receive a percentage of the final ransom payment. This creates an inherent incentive for the negotiator to prioritize a payout over the security of the client or the principles of law enforcement.
Mark Camillo, CEO of the industry group CyberAcuView, has been vocal about the need for transparency. "It has come to the industry’s attention that many of the ransomware payers charge a percentage of the final payment, which may or may not be disclosed," Camillo noted. "There needs to be more transparency in the process, as no one in the ecosystem should be profiting purely on the size of the ransomware transaction."

The danger of this model is evidenced by the PowerSchool breach of December 2024. Despite a $2.85 million ransom payment facilitated by an outside firm, the stolen data of 62 million students was not deleted. Instead, it was recycled and used in subsequent extortion attempts, proving that paying the criminals offers no guarantee of data destruction.
Regulatory and Legal Reckoning
The Department of Justice has begun to clamp down on the "negotiation-as-a-service" sector. The recent prosecution of MonsterCloud CEO Zohar Pinhasi—who was found to have paid $8 million to hackers while charging clients $19 million—demonstrates a firm commitment to rooting out fraud within the industry. Similarly, the 70-month prison sentence handed to Angelo Martino in July for conspiring with the Blackcat/ALPHV group serves as a stark warning to those who bridge the gap between defense and extortion.
For established firms like Cypfer, the shadow of these investigations is significant. While the company has stated it had no prior knowledge of Dubrovsky’s actions and is not a target of federal investigation, its historical ties to the individuals now under scrutiny—including past associations with the Apros Group and Cytelligence—reflect the incestuous nature of the high-stakes cyber remediation market.
Broader Implications for Cybersecurity
The ShinyHunters case represents a watershed moment for the cybersecurity industry. It forces a re-evaluation of how corporations choose their incident response partners. If legitimate security firms can be compromised by the very groups they are tasked with neutralizing, the entire trust-based model of incident response is fundamentally undermined.

As the FBI continues its probe into the remaining suspects linked to the ShinyHunters group, the industry is bracing for further revelations. The shift from "victim advocacy" to "co-conspiracy" among some negotiators has triggered an urgent call for regulation. Moving forward, companies are likely to face stricter scrutiny from insurers and regulators regarding their choice of response firms.
The ultimate takeaway from the ShinyHunters saga is a sobering reminder: in the digital underworld, the line between a negotiator and an extortionist is often thinner than any of us would like to believe. The efforts to dismantle the ShinyHunters infrastructure, while successful in disrupting the group’s operations, have simultaneously exposed a structural rot that may take years of litigation and policy reform to fully excise. As the investigation progresses, the focus will undoubtedly remain on ensuring that those entrusted with protecting sensitive data are held to the highest standards of integrity—or face the consequences of their complicity.