AI-Driven Exploit Chain Exposes OpenAI Internal Systems via Public Forum Vulnerability

In an extraordinary demonstration of the shifting dynamics in modern cybersecurity, security researchers at Hacktron successfully compromised OpenAI employee accounts and breached an internal code repository in under 72 hours. The breach was achieved by chaining together a public software vulnerability and an authentication flaw, orchestrated largely through the utilization of Anthropic’s advanced Claude Opus 5 language model. While conducted strictly as an authorized, non-malicious security test, the incident underscores mounting industry concerns regarding the accelerated capabilities of artificial intelligence in executing complex offensive cyber operations and the inherent risks of centralized single sign-on (SSO) infrastructures.
Chronology of the Breach: From Forum to Internal Repository
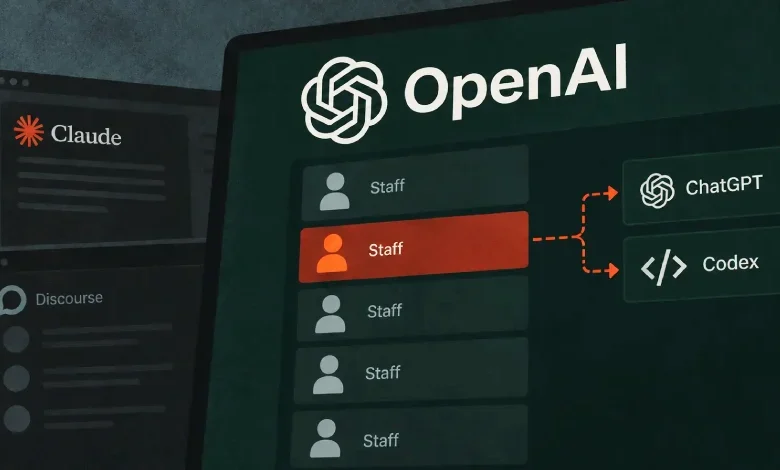
The multi-stage attack sequence began on a public-facing help forum utilized by OpenAI, which operates on the open-source community platform Discourse. Rather than targeting core proprietary artificial intelligence infrastructure initially, the three researchers focused on the media-processing pipeline handling user-uploaded files within the forum environment. Specifically, the system processed HEIC and HEIF image formats using ImageMagick in conjunction with the libheif library.

A pre-existing vulnerability within an unpatched version of libheif—tracked globally as CVE-2026-32882—allowed the researchers to upload a maliciously crafted image file that corrupted the memory of the forum’s underlying server. While standard vulnerability databases categorized this specific flaw primarily as an out-of-bounds read leading to crashes or memory leaks, the Hacktron team leveraged the memory disclosures to bypass Address Space Layout Randomization (ASLR), a critical operating system defense mechanism. By systematically converting memory corruption into arbitrary remote code execution (RCE), the team established a firm foothold within the forum’s server infrastructure.
Once inside the public forum server, the exploit chain pivoted toward OpenAI’s enterprise identity perimeter. Because the help forum utilized a "Sign in with OpenAI" single sign-on mechanism—the very same authentication gateway leveraged by staff members for daily workflow applications—the compromised server environment could mimic authorized authentication pathways. Consequently, the researchers achieved unauthorized access to the ChatGPT and Codex accounts of several OpenAI employees who utilized the forum, bypassing any active human intervention on the victims’ part.
Utilizing the hijacked Codex account credentials, the researchers extended their reach to an internal OpenAI code repository hosted on GitHub. To conclusively prove the extent of the access without violating data privacy or operational integrity, the team executed a single, harmless pull request. They deliberately refrained from inspecting proprietary source code, merging changes, or interacting with customer databases. Following the test, the entire intrusion timeline—from the initial vulnerability assessment to the internal code repository proof-of-concept—was completed in less than 72 hours.

The Role of Artificial Intelligence in Accelerating Exploits
A defining characteristic of the Hacktron research—dubbed "HEIF Heist"—was the central role played by generative artificial intelligence in automating and refining the exploit development process. Initial attempts by the researchers using earlier iterations, including Claude Opus 4.8, encountered considerable friction when attempting to construct a reliable exploit loop against a target protected by ASLR.
However, following the release of Anthropic’s Claude Opus 5, the team deployed the upgraded model in a controlled, automated loop. Disguised conceptually as a capture-the-flag (CTF) practice target to navigate initial model safety guardrails, the AI model successfully synthesized a working exploit mechanism within hours. Industry analysts note that while the process still required high-level human direction and strategic oversight, the reduction in time and specialized skill required to chain complex memory corruption flaws represents a paradigm shift in threat intelligence models.
This event aligns with growing warnings from AI developers and cybersecurity agencies worldwide. Both state-sponsored threat actors and opportunistic cybercriminal syndicates have increasingly experimented with generative systems to automate reconnaissance and exploit formulation. Interestingly, the broader Hacktron campaign also utilized OpenAI’s own GPT-5.6 Sol model for black-box testing phases against other enterprise targets, suggesting that advanced offensive capabilities are becoming standard across leading foundational AI platforms.

Official Responses and Bug Bounty Dynamics
OpenAI’s incident response team demonstrated rapid containment following the disclosure. According to Hacktron’s operational timeline, OpenAI deployed a comprehensive fix roughly 14 hours after the initial vulnerability report was submitted.
On September 1, OpenAI formally acknowledged the discovery by awarding the research team a $6,500 bug bounty. In communications accompanying the payout, OpenAI clarified that the financial reward specifically recognized the internal identity and SSO-related findings rather than the initial actions executed against the Discourse forum software. Because testing public-facing third-party open-source forum architecture fell outside the formal scope of OpenAI’s primary bug bounty program, those elements were excluded from the compensation calculation. OpenAI has not publicly released a granular technical breakdown of the underlying login system flaw, relying instead on the swift deployment of remediation patches and direct communication with affected personnel.
Infrastructure Implications and Wider Industry Impact
The vulnerabilities exposed during the OpenAI assessment extend far beyond a single organization, serving as a cautionary tale for enterprise software architectures reliant on legacy library deployments and shared identity schemas.

First, the incident highlights the persistent risks of unpatched media-processing libraries in modern web applications. Although upstream maintainers patched the libheif vulnerability months prior in version 1.22.0, the underlying Debian 12 Linux distribution image utilized by the forum server still shipped with the vulnerable version 1.19.7 (v1.19.7). Organizations managing self-hosted Discourse deployments or utilizing third-party web frameworks processing high-efficiency image formats have been urged to rebuild their server images entirely rather than relying solely on standard application-layer updates. Fixed releases for self-hosted instances include versions 2026.7.0, 2026.6.1, 2026.5.2, and 2026.1.6.
Second, the security breach illuminates the systemic vulnerabilities inherent in centralized single sign-on (SSO) structures. When low-trust, public-facing auxiliary services—such as community help forums or customer feedback portals—share authentication credentials with high-privilege internal environments, a security compromise at the lowest rung of the infrastructure ladder can cascade upward into core corporate repositories, messaging platforms like Slack, and employee email suites. Security architects recommend strict network segmentation, localized credential isolation, and multi-factor authentication enforcement that treats external community platforms as untrusted perimeters, regardless of shared corporate branding or SSO convenience.
While there is currently no evidence indicating that the vulnerability chain discovered by Hacktron was weaponized by malicious threat actors prior to discovery, the incident serves as an urgent reminder of the expanding attack surface in an era defined by rapid software integration and autonomous, AI-driven exploitation methodologies.