Google and Industry Partners Dismantle Massive XCPE Botnet Targeting Millions of Android TV Devices

In a significant collaborative operation, Google’s Threat Intelligence Group (GTIG) has successfully dismantled a sprawling, global botnet known as XCPE. This sophisticated malicious network, which leveraged pre-infected Android-based set-top boxes to conduct advertising fraud and facilitate illegal residential proxy services, compromised an estimated 1.3 million devices worldwide. Beyond the immediate tally of infected TV boxes, security experts warn that the infrastructure supporting the botnet provided a gateway to more than 10 million additional devices, including IoT-connected healthcare hardware, digital signage, and specialized appliances like karaoke machines.
The takedown follows a months-long investigation into the supply chain practices of Videostrong Technology Co., a Chinese hardware manufacturer. Google confirmed that it has officially severed all ties with the firm after determining that the company intentionally embedded malware into its firmware. This clandestine software activated the moment a user connected their new device to the internet, turning unsuspecting consumers into unwitting participants in a global cyber-criminal enterprise.
Anatomy of the XCPE Infection
The XCPE botnet operated by effectively "hijacking" the internet connections of residential users. By installing a persistent backdoor, the malware allowed the device’s IP address to be resold through various residential proxy networks. These networks are highly coveted by malicious actors because they provide "clean" residential traffic, allowing attackers to mask their true locations, bypass geographic restrictions, automate large-scale account takeovers, and scrape proprietary data for AI training models without triggering traditional security defenses.
According to researchers, the malware was not merely a passive conduit for traffic. Videostrong allegedly monetized these backdoors by selling access to criminal affiliates, who used the infected boxes as a distribution platform for further malicious modules. These modules could transform a home entertainment device into a launchpad for credential stuffing, ad fraud, or distributed denial-of-service (DDoS) attacks.
Chronology of the Threat and Investigation
The discovery of the XCPE botnet is the culmination of a broader effort to secure the fragmented Android IoT ecosystem. The timeline of this threat spans several years, characterized by rapid evolution in how malware is delivered to consumer electronics.

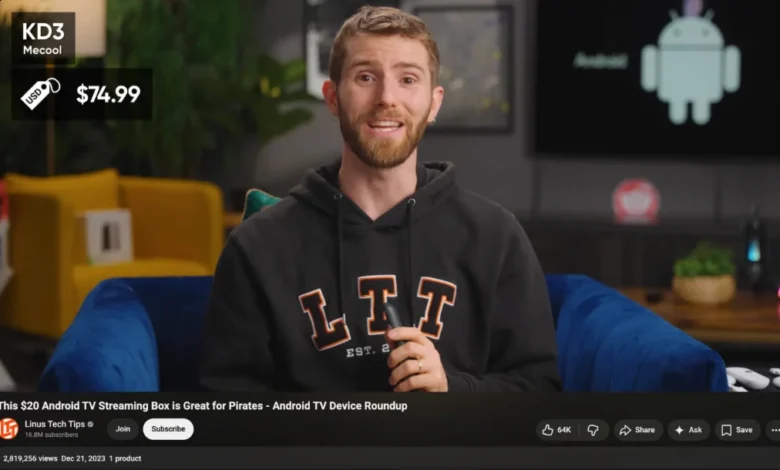
- 2023: MECOOL set-top boxes gain massive popularity, aided by endorsements from influential YouTube channels, including Linus Tech Tips. While these devices were marketed as high-performance streaming solutions, they were secretly bundling the very malware that would later form the backbone of the XCPE network.
- January 2026: Security firm Synthient publishes research on the "Kimwolf" botnet, which utilized vulnerabilities in residential proxy services to compromise devices on local networks. This research highlighted how easily a single infected set-top box could pivot to infect other connected hardware.
- July 2026: Federal law enforcement, including the FBI, disrupts the "Popa" botnet, which had been utilizing similar tactics through the Israeli-based proxy provider NetNut.
- October 2026: Oxylabs and Honeygain, two prominent entities in the proxy space, undergo a corporate reorganization under the "Source" brand, following significant private equity investment.
- November 2026: Google officially announces the disruption of the XCPE botnet and confirms its break from Videostrong Technology Co.
The Role of Residential Proxy Providers
The GTIG report identifies a disturbing trend: the integration of official software development kits (SDKs) from legitimate residential proxy companies into malicious firmware. While providers such as AppSalt (Honeygain) and NetNut argue that their services are designed for ethical data collection, their business models have repeatedly been exploited by botnet operators.
In the case of XCPE, the malware forced devices to connect to these proxy networks without the owner’s knowledge or consent. This presents a unique challenge for cybersecurity professionals: the difference between a "legitimate" proxy node and a "botnet" node often rests on a consent mechanism that can be easily spoofed by malicious developers.
Oxylabs, in a post-publication statement, acknowledged that their systems were being used in this capacity. "We have been conducting regular audits of the applications provided by our partners," the company stated. "However, following this incident, we will improve the application’s build fingerprinting logic to better detect cases where the SDK is running on an unapproved build." Oxylabs emphasized that the supplier involved in the XCPE infection accounted for less than 1% of their IP address pool and that they had terminated the relationship upon discovering the breach.
Broader Implications for IoT Security
The XCPE incident underscores a fundamental failure in the security lifecycle of low-cost IoT hardware. Because many of these devices are manufactured with little oversight, the "initial boot-up" process has become the most dangerous moment for a consumer.
Google noted that it requires Android device makers to pass rigorous security and compatibility tests. However, manufacturers like Videostrong bypassed these protections by pushing malicious updates or installing hidden partitions immediately after the device was first connected to a network. While Google claims to have addressed the specific vulnerability used by Videostrong, the industry remains wary of the sheer volume of "bad-box" operations still in circulation.
The involvement of the Motion Picture Association (MPA) in the investigation highlights another layer of the crisis: the prevalence of pirated streaming services. Many of these infected boxes are purchased specifically because they offer access to unauthorized content. Consumers who purchase "all-in-one" streaming boxes from non-reputable vendors are essentially trading their network security for access to illegal content, creating a self-sustaining cycle where the user is both a victim and a participant in criminal activity.

Analysis: A Call for Supply Chain Accountability
The XCPE botnet is likely just one piece of a larger puzzle. As Ben Brundage, founder of Synthient, noted, the 1.3 million figure provided by Google is likely a "highly conservative" estimate. Given the diverse distribution channels used by proxy affiliates, the total number of compromised units—including telehealth devices and digital signage—could be exponentially higher.
The implications for the average consumer are significant. An infected set-top box can act as an entry point for lateral movement within a home network, potentially exposing laptops, smartphones, and sensitive smart-home devices to surveillance or data theft. For corporate networks, the threat is even more acute, as these devices can be used to bypass corporate firewalls or facilitate large-scale credential harvesting.
Industry experts suggest that the solution requires a three-pronged approach:
- Hardware Verification: Increased scrutiny of white-label manufacturing in the IoT space to ensure that the firmware shipped to customers matches the code audited by platform owners.
- Proxy Industry Reform: Stricter "Know Your Customer" (KYC) requirements for residential proxy providers to prevent bad actors from masking their traffic through consumer hardware.
- Consumer Awareness: Greater education regarding the risks of "too-good-to-be-true" streaming hardware. Devices that promise free access to premium content through back-door channels are frequently subsidized by the very botnet operators that steal the user’s data and bandwidth.
As the digital landscape continues to integrate more IoT devices into the home and office, the XCPE botnet serves as a stark reminder that security cannot be an afterthought. The transition from a "connected device" to a "compromised asset" can happen in seconds, often without a single visual indicator to the user. Moving forward, the focus of tech giants and law enforcement must remain on the supply chain—the source where the malware is baked into the silicon—rather than merely patching the symptoms of these massive, automated networks after the damage is done.