Three Sophisticated Threat Clusters Target Russian Enterprises with Advanced Malware, Ransomware, and Custom Backdoors

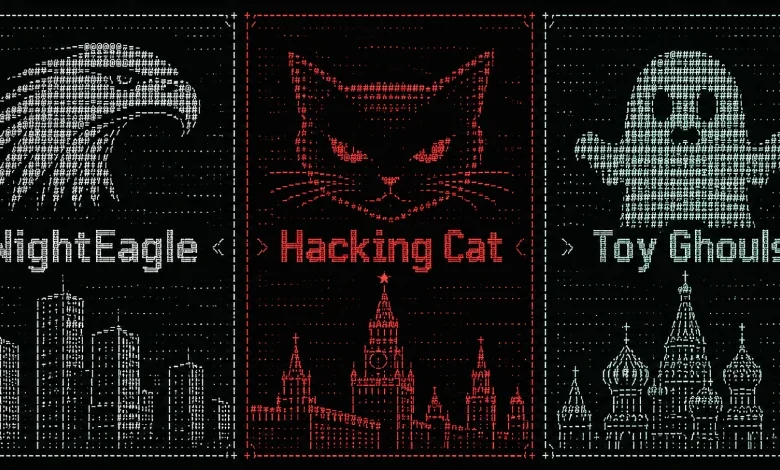
Russian commercial and governmental enterprises have increasingly become the primary focus of three distinct cyber-espionage and hacktivist threat activity clusters. According to comprehensive technical telemetry and forensic analysis published by global cybersecurity vendor Kaspersky, these groups—identified as NightEagle, Hacking Cat, and Toy Ghouls—have deployed an array of sophisticated tactics, techniques, and procedures (TTPs). Their campaigns involve everything from modular backdoors targeting Microsoft Exchange servers to multi-platform ransomware, wipers, and unconventional command-and-control (C2) communication channels utilizing MQTT brokers and messaging applications.
As the geopolitical landscape continues to heavily influence the digital sphere, the convergence of state-sponsored espionage techniques and ideologically motivated hacktivism has created a volatile threat environment for organizations operating within Russia. The findings underscore a broader trend: the democratization of high-level offensive cyber capabilities, where open-source components, artificial intelligence assistance, and modular frameworks are routinely leveraged to compromise complex corporate networks.
The NightEagle APT Campaign: Deep Network Intrusion and Exchange Server Exploitation
The NightEagle threat group, tracked by intelligence analysts under the alternate designation APT-Q-95, has maintained an active presence since at least 2023. Initially recognized for targeted attacks against government agencies and high-technology firms in Asia, the group has evolved its operational methodology to target Russian corporate entities. Recent investigations by Kaspersky indicate that NightEagle relies heavily on compromised legitimate credentials to breach corporate Virtual Private Networks (VPNs).
To obscure their geographic origin and bypass perimeter defenses, the attackers frequently route their connections through Cloudflare WARP tunnels configured within the Russian IP space, alongside virtual infrastructure providers located across Europe. Once initial access is secured, NightEagle deploys GhostContainer, a sophisticated modular backdoor engineered specifically to infiltrate Microsoft Exchange servers.
GhostContainer grants operators pervasive, uninhibited access to compromised mail servers. It facilitates arbitrary code execution, granular file system manipulation, and the dynamic loading of supplementary plugins. Designed to blend seamlessly with standard network traffic, the malware masquerades as a routine server component while simultaneously functioning as a traffic redirection proxy or tunneling utility.
The architecture of GhostContainer reveals a heavy reliance on publicly accessible open-source repositories found on GitHub. Its codebase incorporates elements from the Neo-reGeorg tunneling tool, exploits targeting the CVE-2020-0688 Microsoft Exchange vulnerability, and the GhostWebShell class derived from the ysoserial utility. Although the precise initial delivery vector remains under investigation, forensic evidence suggests the threat actors extract server cryptographic keys from ASP.NET configurations, overwrite the VIEWSTATE framework parameter, and inject the payload directly into system memory to initiate execution without dropping traditional file artifacts onto the disk.
Upon establishing a foothold, NightEagle focuses intensely on lateral movement and privilege escalation. The group has been observed utilizing Microsoft developer tunnels alongside the open-source utility rdp2tcp to tunnel Remote Desktop Protocol (RDP) traffic. Furthermore, the operators systematically exploit historical Active Directory vulnerabilities, such as the infamous BlueKeep flaw (CVE-2019-0708), to fabricate local administrative accounts and execute DCSync attacks designed to impersonate domain controllers. The ultimate objective of the NightEagle cluster is long-term persistence, the harvest of domain password hashes, and the deployment of enduring Kerberos tickets to achieve total domination over the victim’s entire Active Directory ecosystem.

Hacking Cat and Pro-Ukrainian Hacktivism: From Defacements to Destructive Malware
Operating in stark contrast to the espionage-driven motives of NightEagle, the pro-Ukrainian hacktivist collective known as Hacking Cat has undergone a dramatic operational evolution. Active since February 2024—initially focusing on low-impact website defacements and opportunistic data breaches—the group shifted its strategy toward aggressive encryption and destructive attacks against Russian infrastructure.
Kaspersky’s intelligence reports highlight that Hacking Cat frequently collaborates with allied hacktivist entities, including the Cyber Anarchy Squad and the Ukrainian Cyber Alliance. This cooperative ecosystem often muddies traditional attribution frameworks, as multiple groups share overlapping toolkits and operational infrastructure.
In their campaigns against Russian enterprises, Hacking Cat has weaponized critical vulnerabilities affecting Microsoft Exchange servers, notably CVE-2021-26855 and CVE-2026-42897. Successful exploitation leads to the deployment of Gorilla RAT, a remote access trojan authored in the Go programming language. Gorilla RAT establishes outbound connections to remote C2 infrastructure, registers the compromised host, and awaits operator directives to execute shell commands, harvest system telemetry, enumerate running processes, transfer files, and establish robust TCP tunnels.
Beyond espionage tools, Hacking Cat has propagated various iterations of a multi-platform ransomware family designated as Monkey. Written across diverse programming languages including Rust, .NET, C++, and Golang, Monkey variants target Windows, Linux, and VMware ESXi virtualization environments. Emerging in the late summer of 2025, the ransomware incorporates sophisticated routines to terminate non-essential system processes and disable automated recovery mechanisms prior to file encryption.
Notably, a Rust-based variant of the Monkey ransomware employs the ChaCha20-Poly1305 encryption algorithm driven by a locally generated 32-byte key. In certain instances analyzed by security researchers, the malware fails to securely store or transmit the encryption key—effectively transforming the ransomware into a destructive wiper while still leaving standard extortion notes behind. Conversely, other variants store the key locally but omit critical communication channels or cryptocurrency wallet addresses from the ransom note.
Security analysts analyzing the Golang iterations of Monkey identified functional anomalies, such as the inclusion of routines designed to delete Volume Shadow Copies—a capability entirely redundant within Linux and ESXi environments. This technical oversight has led researchers to theorize that the threat actors may have accelerated their development lifecycles through the improper integration of artificial intelligence coding assistants.
Collaboration remains a hallmark of Hacking Cat’s operational model. Alongside the Ukrainian Cyber Alliance, the group has deployed Nemo Wiper, a destructive utility that overwrites target files with randomized byte sequences while filling remaining disk space with dummy files bearing random alphanumeric titles and a .lock file extension. Additionally, joint operations with the Cyber Anarchy Squad have facilitated the distribution of ClearWater ransomware via automated batch scripts, pointing toward a Ransomware-as-a-Service (RaaS) model circulating within pro-Ukrainian hacktivist circles.
In response to these public disclosures, representatives from Hacking Cat published statements via their official Telegram channel. The group acknowledged ownership of certain proprietary tooling while explicitly denying involvement in the deployment of specific ransomware lockers, accusing security vendors of misattributing tools to unrelated actors.

Toy Ghouls and Custom Tooling: The Shift to Bespoke Backdoors
Rounding out the trio of threat actors targeting Russian organizations is the financially motivated group Toy Ghouls, also tracked under aliases such as Bearlyfy, Laboo.boo, and Feral Wolf. Active since 2025, the group initially relied on readily available, leaked builders associated with well-known ransomware strains like Babuk and LockBit. However, as defensive postures hardened, Toy Ghouls transitioned to developing proprietary solutions, initially introducing their custom GenieLocker ransomware before pivoting entirely toward bespoke backdoor architectures.
First detected in active campaigns in July 2026, the group’s custom backdoor framework is distributed in distinct operational variants. To facilitate delivery, the actors leverage Windows Remote Management (WinRM) services, utilizing open-source penetration testing utilities such as Evil-WinRM and WinRM-fs to upload the backdoors and associated configuration files directly to targeted endpoints.
One primary variant, designated as Bird Agent, can operate interactively via command-line sessions or establish persistent execution as an authorized Windows service. Upon initialization, the malware searches for an encrypted configuration file named "config.toml" within its working directory. To enforce strict machine-binding and hinder automated sandboxed analysis, the backdoor derives an decryption key directly from the host system’s Registry-stored MachineGuid value. If the configuration fails validation, execution halts immediately.
The configuration parameters dictate how the malware connects to its operators. Depending on the specific campaign variant, the configuration houses either cluster identifiers required to interface with public MQTT brokers like HiveMQ, or internal Matrix-room identifiers alongside authentication access tokens used within the Element messenger platform. If token parameters are omitted during installation, the backdoor dynamically prompts the administrator or operator for input before storing it securely.
Once communication channels are secured, Bird Agent transmits comprehensive host telemetry to the C2 infrastructure. It polls the HiveMQ broker via HTTP GET requests to retrieve remote commands, which are subsequently executed silently via PowerShell with parameters designed to suppress user interaction and profile loading (-NonInteractive -NoProfile -Command). Execution results are then relayed back to the controllers. The Element-based variant operates similarly, though inbound commands are executed directly through the standard Windows command-line shell interface.
Kaspersky analysts emphasized that the adoption of non-traditional communication mediums—such as MQTT message brokers and Matrix-based messaging apps—represents a strategic evolution. By abandoning reliance on conventional web servers and public open-source projects in favor of custom-built, application-layer tunneling, Toy Ghouls aims to blend covert communications with legitimate network traffic, thereby extending dwell times and evading automated behavioral detection systems.
Broader Implications and Enterprise Defense Recommendations
The concentrated focus of NightEagle, Hacking Cat, and Toy Ghouls on Russian enterprises highlights a rapidly maturing cyber threat landscape where ideological motivations, financial incentives, and state-backed espionage intersect. The convergence of multi-stage infection chains, shared developer repositories, and AI-assisted malware generation demonstrates that modern threat actors are continuously lowering the barriers to entry for advanced cyber operations.
For corporate security teams and enterprise network defenders, these campaigns reinforce the necessity of adopting rigorous, defense-in-depth security postures. Key remediation and mitigation strategies recommended by cybersecurity authorities include:
- Strict Identity and Access Management: Enforcing multi-factor authentication (MFA) across all corporate VPN gateways and remote access endpoints to mitigate the risks associated with compromised credentials.
- Proactive Patch Management: Rapidly applying security updates for critical perimeter infrastructure, particularly Microsoft Exchange servers, to close known exploitation vectors like CVE-2020-0688, CVE-2021-26855, and CVE-2026-42897.
- Active Directory Hardening: Regularly auditing Active Directory configurations to identify and remediate privilege escalation paths, unauthorized local account creation, and potential DCSync exposure.
- Network Segmentation and Monitoring: Implementing comprehensive egress filtering and monitoring anomalous outbound traffic patterns—such as unauthorized connections to MQTT brokers, messaging platforms, or unusual tunneling protocols—to disrupt command-and-control communications early in the kill chain.