Dutch authorities arrest convicted hacker Pepijn van der Stap in escalating ShinyHunters investigation

The arrest of 24-year-old Dutch national Pepijn van der Stap on September 16 marks a critical juncture in the ongoing international investigation into the prolific cybercriminal collective known as ShinyHunters. Authorities in the Netherlands apprehended van der Stap—a figure previously convicted in 2023 for extensive data theft and extortion—on suspicion of facilitating the group’s most recent and brazen campaigns. The arrest has triggered a volatile reaction from the remaining members of ShinyHunters, who have responded with a series of high-profile attacks against government and corporate entities, including the United States Federal Bureau of Investigation (FBI) and the Russian-linked ransomware syndicate Cl0p.
Van der Stap, a resident of Almere and Lelystad, has long been a dual-faced figure in the cybersecurity landscape. During his 2023 trial, he famously described his life as a modern iteration of the Dr. Jekyll and Mr. Hyde narrative. By day, he operated as a software engineer for the Amsterdam-based cybersecurity startup Hadrian and contributed as a volunteer for the Dutch Institute for Vulnerability Disclosure (DIVD). By night, under the pseudonym Umbreon, he allegedly weaponized his technical skills to exfiltrate and extort victim data on illicit forums like RaidForums and Breached. Prosecutors estimated his previous illicit activities generated between €1.5 million and €2.7 million. Following a four-year sentence, with one year suspended, he was released in December 2025, claiming to be a reformed individual attempting to reconcile his past through restitution and legitimate employment at Neo Security.
A Chronology of Escalation
The recent surge in activity began in February 2026, when a native Dutch-speaking member of ShinyHunters successfully social-engineered an employee at Odido, the Netherlands’ largest mobile telecommunications provider. The intrusion, which led to the theft of sensitive data belonging to more than 6.2 million Dutch citizens, prompted the Dutch police to release audio of the attacker in a public appeal for identification. ShinyHunters confirmed via media statements that the individual in the audio was indeed one of their own, signaling a departure from the group’s typically clandestine behavior.

The timeline of recent events suggests a coordinated effort by the group to demonstrate resilience in the face of law enforcement pressure:
- February 2026: ShinyHunters compromises Odido, exfiltrating personal data of over 6.2 million Dutch citizens.
- September 9, 2026: Pepijn van der Stap gives an interview to security researchers, maintaining his status as a reformed hacker.
- September 16, 2026: Dutch authorities arrest van der Stap at his residence, seizing hardware and records.
- September 20–22, 2026: ShinyHunters claims credit for a breach of the FBI’s job application portal (apply.fbijobs.gov), leaking data on 5,000 officials.
- September 25, 2026: Mandiant and Google Threat Intelligence Group (GTIG) publish findings on mass exploitation of the Oracle PeopleSoft vulnerability by ShinyHunters.
- September 29, 2026: Scheduled court appearance for van der Stap in the Rotterdam District Court.
The Weaponization of PeopleSoft
The recent breach of the FBI job portal was not an isolated incident but part of a sophisticated, large-scale campaign targeting the Oracle PeopleSoft platform. ShinyHunters reportedly exploited CVE-2026-35273, a vulnerability that Oracle patched earlier this year. Despite early warnings and the release of web application firewall (WAF) rules by security firms like Mandiant, ShinyHunters managed to bypass these mitigations using advanced URL-encoding techniques.
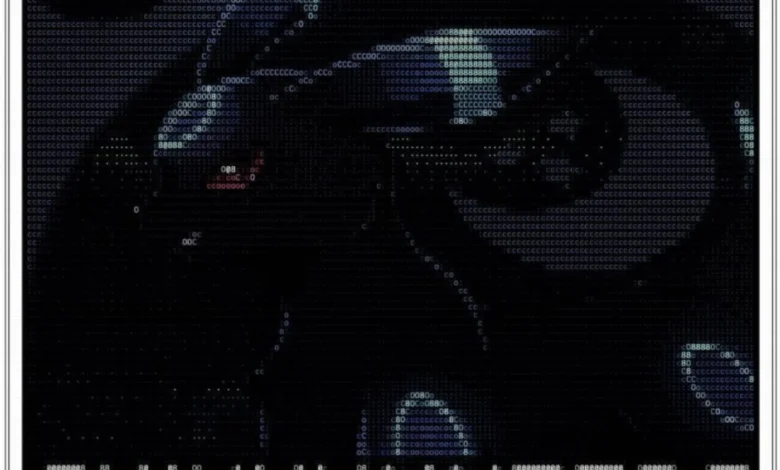
The scope of this campaign is extensive. According to Mandiant and Google researchers, the group has utilized this exploit to penetrate dozens of organizations across sectors including agriculture, healthcare, technology, and government. The stolen FBI data was particularly sensitive, including personal identifiers of agents investigating foreign state-backed cyber threats and psychiatric files of bureau staff. The inclusion of an ASCII art design of the character "Umbreon" on the defaced FBI site serves as both a signature and a potential redirection of blame toward van der Stap by current group leadership.
Internal Power Dynamics: The Role of "Rey"
Intelligence sources suggest that the aggressive pivot in ShinyHunters’ tactics is the result of a leadership vacuum and subsequent takeover by a teenage hacker operating out of Amman, Jordan, known by the handle "Rey." Rey is a central figure in the ScatteredLapsussHunters (SLSH) group, an entity formed through the merger of Scattered Spider, LAPSUS$, and ShinyHunters.

The relationship between Rey and van der Stap appears to be marked by animosity. Observers note that the use of the Umbreon avatar in the FBI defacement is a tactical maneuver intended to implicate van der Stap in the new wave of attacks, potentially as a form of retaliation for internal disputes over the control of stolen data repositories and monetization strategies. Rey, whose identity was first publicly linked to cybercrime by the firm KELA in 2025, has maintained a provocative social media presence, taunting law enforcement and rival cybercrime groups alike.
Implications and Broader Impact
The implications of this transition in leadership and the ongoing law enforcement focus are significant for the global cybersecurity landscape. Mandiant researchers estimate that ShinyHunters is on a trajectory to generate nearly $100 million in illicit revenue in 2026 alone. This massive influx of capital has allowed the group to professionalize their operations, including providing legal support for members—a level of organization rarely seen in decentralized hacking collectives.
The "bad blood" between SLSH and other groups, such as the now-diminished TeamPCP, highlights the fragility of alliances in the underground economy. Partnerships formed to monetize supply-chain compromises often collapse when one party feels cheated. In this case, ShinyHunters’ decision to "go rogue" and extract value from TeamPCP’s stolen credentials without providing a share of the proceeds has created a fractured landscape where groups are as likely to attack each other as they are to target corporations.
Furthermore, the incident at the Dutch Institute for Vulnerability Disclosure (DIVD)—where van der Stap previously volunteered—has sparked internal security reviews. While the nonprofit reported an incident involving the malicious use of artificial intelligence, they have officially distanced the event from the actions of their former volunteer or the ShinyHunters group.

Official Responses and Future Outlook
The Dutch police, in a statement released via their official X (formerly Twitter) account, confirmed the arrest of a 24-year-old suspect linked to the investigation. The suspect is expected to face the Rotterdam District Court, where prosecutors will likely present evidence linking him to the recent wave of extortions.
The defiance displayed by ShinyHunters in their public statements—calling the Dutch police "incompetent" and "irrelevant"—underscores the challenge facing international law enforcement. The group’s ability to recruit talent, manage finances, and rapidly pivot between zero-day exploits suggests that traditional law enforcement methods, while effective at capturing individual actors, may struggle to dismantle the underlying infrastructure of the SLSH network.
For cybersecurity professionals and corporate security teams, the case of Pepijn van der Stap serves as a stark reminder of the "insider threat" model. The ease with which an individual can transition between security researcher and criminal highlights a growing vulnerability in the industry. As the FBI and other international agencies continue to investigate the breach of the Oracle PeopleSoft platform, the focus will likely remain on whether these arrests can disrupt the group’s momentum or if the leadership of figures like "Rey" will continue to fuel an era of unprecedented cyber aggression. The coming weeks, beginning with van der Stap’s court proceedings, will be pivotal in determining the extent to which authorities can curb the influence of a group that has effectively weaponized both stolen data and the public narrative surrounding its own members.