
flaw
-
Cloud Computing
A zero-click RCE flaw in AI coding agents could have exposed enterprise systems
The vulnerability stems from the way these agents handle external extensions. To enhance productivity, developers often install plugins that allow…
Read More » -
Cybersecurity
Acronis Warns of Actively Exploited High-Severity Flaw in cPanel and Plesk Backup Plugin
Cybersecurity and data protection firm Acronis has issued an urgent advisory warning administrators of a high-severity local privilege escalation vulnerability…
Read More » -
Cybersecurity
China-Aligned Espionage Group Exploits Critical Tencent Sogou Input Method Flaw to Deploy GrayRabbit Backdoor
A sophisticated China-aligned threat actor has been actively exploiting a critical, one-click remote code execution vulnerability in Tencent’s immensely popular…
Read More » -
Cybersecurity

GitLab Issues Emergency Patches for Maximum-Severity Path Traversal Flaw Under Active Exploit
GitLab has officially released critical security updates to remediate multiple vulnerabilities across its ecosystem, most notably a maximum-severity path traversal…
Read More » -
Cybersecurity
Skullcandy Dime 3 Wireless Earbuds Exposed to Bluetooth Hijacking Due to Unpatchable Firmware Flaw
The Carnegie Mellon University CERT Coordination Center (CERT/CC) has issued a critical advisory warning that the popular Skullcandy Dime 3…
Read More » -
Cybersecurity
Russian State-Supported Group Exploits Zero-Day Zimbra Flaw for Months of Western Webmail Espionage
A sophisticated Russian state-supported espionage group has spent a staggering five months surreptitiously accessing and exfiltrating sensitive data from Western…
Read More » -
Cybersecurity
RefluXFS: Critical Linux Kernel Flaw Allows Unprivileged Local Users to Gain Persistent Root Access on XFS Filesystems
A significant vulnerability in the Linux kernel, dubbed RefluXFS and tracked as CVE-2026-64600, was publicly disclosed on July 22, revealing…
Read More » -
Cybersecurity
Apple Patches Critical Hide My Email Flaw That Exposed User Identities, Faces Class Action Lawsuit
Apple has successfully addressed a significant security vulnerability within its "Hide My Email" service, a premium feature designed to bolster…
Read More » -
Cybersecurity
Hackers Actively Exploit Critical SharePoint RCE Flaw (CVE-2026-50522) to Steal Machine Keys and Maintain Persistent Access
A critical vulnerability, identified as CVE-2026-50522, within Microsoft SharePoint is being actively exploited by malicious actors, posing a severe and…
Read More » -
Cybersecurity
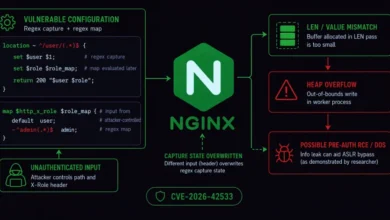
F5 Ships Urgent Fix for Critical NGINX Remote Code Execution Flaw
F5, a leading application security and delivery company, has released critical patches for a severe vulnerability in NGINX, identified as…
Read More »
