The Managed Service Provider (MSP) sector, long characterized by its low barrier to entry and rapid, organic growth, is currently navigating an existential shift. For decades, the industry has operated in a largely self-defined ecosystem where technical proficiency was validated by vendor-specific certifications or anecdotal client success. However, as MSPs become the primary custodians of sensitive corporate infrastructure, intellectual property, and high-stakes cybersecurity environments, the lack of a universal professional standard has moved from a minor industry quirk to a significant business risk.
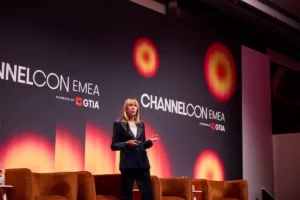
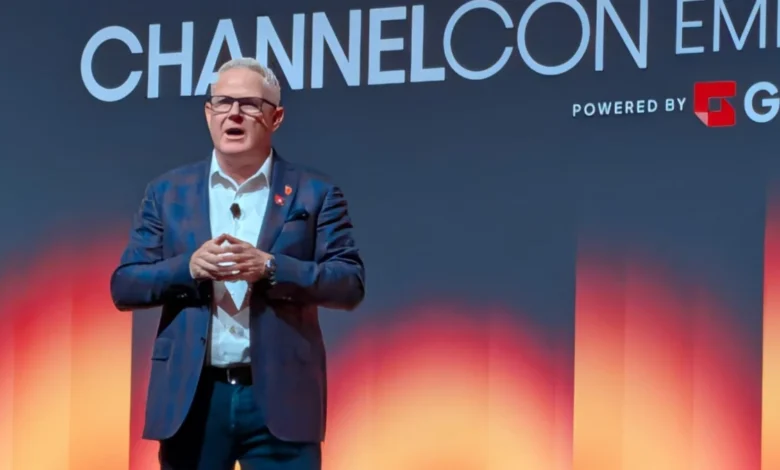
Dan Wensley, CEO of the Global Technology Industry Association (GTIA), has signaled that the time for fragmented self-definition is ending. Speaking at the GTIA ChannelCon EMEA event in London, Wensley highlighted a fundamental vulnerability in the current IT service landscape: the ease with which any entity can market itself as a comprehensive, high-security MSP without adhering to a verified, third-party framework of operational excellence.
The Erosion of the Wild West Model
The traditional model of the MSP industry has been defined by entrepreneurial agility. Many successful firms grew from one-man shops into mid-sized enterprises, building reputations on reliability and personal relationships. Yet, the modern threat landscape—characterized by sophisticated ransomware-as-a-service (RaaS) groups and the integration of artificial intelligence into daily workflows—has fundamentally changed what it means to be an IT provider.
Today, an MSP effectively holds the “keys to the kingdom” for their clients. If a provider’s security posture is compromised, the impact cascades to dozens or hundreds of downstream businesses. Despite this, there is no standardized metric to measure the efficacy of an MSP’s security delivery or the maturity of their internal operational processes. Clients are often left to navigate a confusing marketplace where a highly sophisticated, security-hardened firm competes on price against a provider with minimal infrastructure and no standardized oversight.
The Genesis of the Consortium for Responsible IT Services
Recognizing that the industry is at a crossroads, the GTIA has formally partnered with the Texas A&M University Global Cyber Research Institute to launch the Consortium for Responsible IT Services. This initiative represents a departure from the ad-hoc standards of the past, aiming to establish a self-regulatory organization (SRO) that functions similarly to professional bodies in accounting or engineering.
The consortium’s mandate is ambitious: to codify professional, operational, and technical standards that transcend individual vendor ecosystems. By moving away from relying solely on certifications from hardware or software vendors—which are often incentivized to promote their own product stacks—the GTIA aims to provide a neutral, peer-reviewed baseline for what constitutes a competent, secure, and responsible service provider.
The development timeline for this framework is estimated at two to three years, a duration reflecting the complexity of reaching a consensus across a global, fragmented industry. During this period, the consortium plans to hold working group meetings, peer-review sessions, and public consultations to ensure the standards are not only rigorous but also practical for firms of varying sizes.
Global Cybersecurity Trends and the Regulatory Shadow
The push for standardization is not occurring in a vacuum. Governments worldwide, particularly in the United Kingdom and the European Union, have begun to view MSPs as critical national infrastructure, given their systemic importance to the economy. In the UK, policymakers have expressed increasing interest in the cybersecurity practices of service providers, noting that the "supply chain attack" vector has become a primary target for state-sponsored and criminal actors.
Wensley’s warning to the industry is stark: "Certification, training, and standards are coming to this industry whether we build them or it is pushed upon us." This perspective is shared by many industry analysts who note that the current legislative trend favors mandatory reporting and stricter compliance audits. By taking the lead, the GTIA hopes to craft a framework that is informed by industry practitioners who understand the nuance of MSP operations, rather than a top-down mandate written by regulators who may lack direct operational context.
Quantitative Realities: Why Standards Matter
The need for this transition is supported by shifting market data. According to recent industry surveys, nearly 60% of small to mid-sized businesses (SMBs) now outsource their IT security entirely to an MSP. However, studies also suggest that SMBs are struggling to distinguish between high-performing security-first providers and those offering superficial coverage.
Furthermore, the rise of the "Cyber-Insurance" market has created a new pressure point. Insurers are increasingly demanding evidence of specific security protocols—such as Multi-Factor Authentication (MFA), endpoint detection and response (EDR), and immutable backups—before underwriting policies for SMBs. MSPs that cannot verify their adherence to these standards are becoming a liability to their clients’ insurance eligibility. A universal standard would provide a clear "seal of approval," simplifying the procurement process for clients and providing a necessary differentiator for MSPs that invest heavily in their internal security posture.
The Road Ahead: Defining Competence
The fundamental challenge for the consortium remains the definition of "competence." What is the baseline for an MSP? Is it the hardware they deploy? Is it the frequency of their security audits? Or is it the maturity of their business continuity planning?
Wensley emphasizes that the standards will not be dictated by a central authority but will emerge from the collective expertise of the GTIA membership. This bottom-up approach is intended to ensure that the standards are achievable for smaller, high-quality firms while remaining stringent enough to provide meaningful protection for clients.
As the industry moves toward this new era of accountability, several key questions remain:
- The Compliance Burden: How will smaller MSPs manage the cost and labor of meeting these new standards?
- The Verification Process: Who will audit the auditors? A self-regulatory body must maintain its own integrity to ensure that the "stamp of approval" carries genuine weight in the market.
- The Competitive Landscape: Will businesses begin to prioritize vendors that carry the SRO designation over those that do not, effectively creating a two-tiered market?
Broader Implications for the Channel
If successful, the GTIA’s initiative could fundamentally alter the economics of the channel. Professionalization often leads to consolidation, as firms that cannot meet higher standards may be forced to merge or exit the market. This could result in a more mature, resilient, and reliable service ecosystem.
The transition toward professional standards also signals a maturation of the IT services industry. For decades, the "IT guy" was viewed as an expense or a technician. Today, the MSP is a strategic partner, a chief information security officer, and a primary defense against digital threats. The establishment of formal standards is the natural, if belated, evolution of a sector that has grown from a niche technical support role into the backbone of the modern digital economy.
As the consortium begins its multi-year development process, the eyes of the global channel are fixed on the outcome. For the MSP, the goal is to demonstrate value; for the client, the goal is to find trust. By bridging this gap with concrete, measurable, and peer-reviewed standards, the GTIA is not just creating a new set of rules—it is attempting to define the professional future of the entire industry. The transition will undoubtedly be complex, but in an era where data is the most valuable asset a company possesses, the move toward professionalization is no longer a matter of choice; it is a matter of survival.
Related posts: