Critical Remote Code Execution Vulnerability Discovered in Alibaba Fastjson 1.x Despite Six Years of Patching

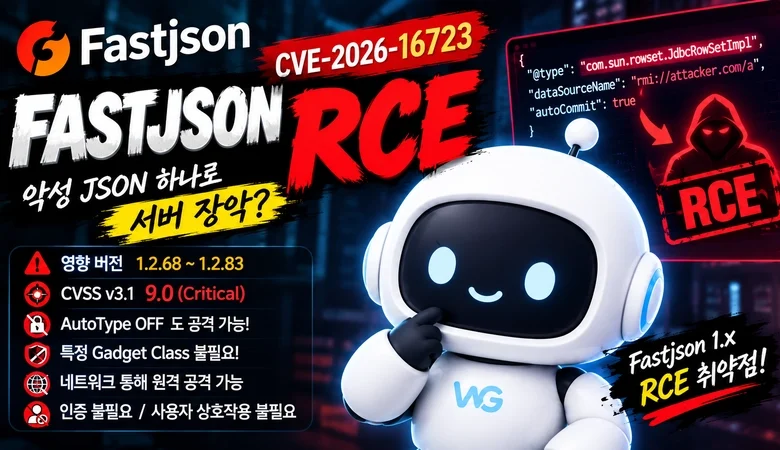
The software development and cybersecurity communities are grappling with a severe security disclosure affecting Alibaba Fastjson versions 1.2.68 through 1.2.83, the final and legacy releases of the widely deployed Java JSON processing library. Designated as CVE-2026-16723 and carrying a critical Common Vulnerability Scoring System (CVSS) rating of up to 9.8, the flaw allows unauthenticated remote attackers to achieve Remote Code Execution (RCE) under default configurations.
What elevates this discovery beyond a routine deserialization bug is its underlying mechanism. The vulnerability can be successfully exploited even when AutoType—Fastjson’s notorious automated class-resolution feature—is disabled, and without relying on any pre-existing dangerous "gadget" classes traditionally required for Java exploitation. Attackers are instead able to construct custom payloads, host them on external infrastructure, and abuse the library’s internal safety validation pathways to execute arbitrary system commands.
Background and Context of the Fastjson Legacy Vulnerability Landscape
Alibaba Fastjson has long been a double-edged sword within the enterprise Java ecosystem. Renowned for its exceptional serialization and deserialization performance, the library achieved massive adoption across global microservices, enterprise architectures, and cloud-native applications, particularly those utilizing the Spring Boot framework. However, this performance came at the cost of continuous security turbulence.

Beginning with CVE-2017-18349, security researchers uncovered a recurring class of vulnerabilities stemming from Fastjson’s ability to dynamically instantiate classes based on type specifiers provided within incoming JSON payloads (the @type directive). Over the span of several years, maintainers implemented multiple layers of defense. These hardening cycles included the introduction of a blocklist, a transition to FNV-1a rolling-hash comparisons, the implementation of a global safeMode kill switch, and strict controls over expected class parameters.
Despite these iterative patches, the architecture of Fastjson 1.x retained legacy assumptions about metadata handling. Because Alibaba formally declared the Fastjson 1.x branch End-of-Life (EOL), directing developers to upgrade to the completely rewritten Fastjson2, no official patch will be released for the vulnerable versions. This leaves countless enterprise applications exposed unless proactive administrative mitigations are enforced.
The Mechanics of CVE-2026-16723: A Two-Stage Remote Fetch
The newly analyzed vulnerability bypasses six successive generations of security hardening by exploiting an overlooked execution path: the metadata-trust branch associated with the @JSONType annotation.
In previous vulnerability scenarios, security controls focused primarily on whether a class name specified in an incoming JSON payload matched a known malicious gadget (such as JdbcRowSetImpl or FileSystemXmlApplicationContext). If the name matched a blocked pattern, execution was halted.

However, CVE-2026-16723 exploits a completely separate code path designed to check whether a given class possesses the @JSONType annotation. The library’s developers originally assumed that this check posed no security risk because it merely inspected class metadata rather than executing arbitrary code.
When Fastjson processes an untrusted JSON payload containing a custom class reference, it attempts to load the class bytes to verify its annotations. In environments running Spring Boot executable fat-JARs, the default class loader is typically LaunchedURLClassLoader, which inherits the capabilities of Java’s standard URLClassLoader. Crucially, this class loader natively supports the jar:http:// URL scheme.
The exploitation vector operates through a deterministic, multi-step chain:
- Payload Transmission: An unauthenticated attacker transmits a crafted JSON payload containing a maliciously constructed URI string in place of a standard Java class path.
- Name-Shape Bypass: Standard name-shape filters, such as
safeModeand hash-based blocklists, fail to recognize the anomalous URI scheme as a dangerous Java class name, allowing it to pass through initial validation gates. - Integer-IP Obfuscation: To bypass string transformations that replace dots (
.) with forward slashes (/), attackers convert standard IPv4 addresses into their 32-bit integer equivalents (e.g., transforming192.168.1.100into3232235876), ensuring the URI remains syntactically valid when processed by Java networking libraries. - First-Stage Remote Fetch: Fastjson calls
getResourceAsStream()on the class loader. This triggers an outbound HTTP connection from the vulnerable server to an attacker-controlled remote server, downloading the compiled bytecode of a custom, attacker-written class (Evil.class). - Metadata Inspection: The library utilizes ASM’s
ClassReaderto parse the downloaded bytecode solely to check for the presence of the@JSONTypeannotation. While this parsing phase does not execute the bytecode, it successfully establishes that the remote fetch succeeded. - JVM-Level Class Loading and Execution: Once the metadata check passes, Fastjson calls
TypeUtils.loadClass(). This invokes the JVM’sdefineClass()mechanism. According to the Java Virtual Machine specification, a class’s static initializer (<clinit>) executes automatically and exactly once the moment the class is prepared for use.
Consequently, the attacker requires no interaction with the class methods and does not need to instantiate the object. The mere act of loading the class forces the JVM to execute the static initializer block, achieving immediate Remote Code Execution.
Timeline of Discovery and Disclosure

While the precise internal timeline of private vulnerability research remains fluid, the public disclosure cycle for CVE-2026-16723 highlights the mounting pressure on legacy software maintenance:
- Historical Context (2022–2024): Following the release of Fastjson 1.2.83, Alibaba officially deprecates the 1.x branch, urging the industry to migrate entirely to Fastjson2.
- Recent Analysis: Independent security researchers and contributors detailed the mechanics of the
@JSONTypemetadata-inspection bypass, demonstrating that remote class loading viaURLClassLoaderremained functional under default configurations. - Current Status: Security advisories are actively circulating across developer platforms, assigning CVSS ratings between 9.0 and 9.8 depending on environmental scoring parameters. Because the library is EOL, no vendor patch is forthcoming.
Fact-Based Analysis of Enterprise Implications
The discovery of CVE-2026-16723 underscores several structural risks inherent in legacy enterprise software dependencies:
- The Perils of Deprecation without Replacement: Millions of enterprise applications continue to run Fastjson 1.2.83 or earlier due to the massive engineering overhead required to refactor legacy codebases to Fastjson2. When an EOL library suffers a critical vulnerability of this magnitude, organizations face a difficult choice between undertaking costly emergency refactoring or implementing imperfect perimeter defenses.
- Assumptions of Safety in Metadata Checks: The vulnerability highlights a classic design flaw in secure coding: treating auxiliary administrative functions—such as annotation scanning and metadata parsing—as security boundaries. Developers must treat all inputs that influence resource resolution, file access, or class loading as inherently hostile, regardless of whether the initial operation appears strictly read-only.
- Network-Level Defense Dependencies: Because application-level patches are unavailable for Fastjson 1.x, organizations are forced to rely on external compensating controls, such as strict egress firewall filtering and network segmentation, to disrupt the remote-fetch stage of the attack chain.
Official Responses and Mitigation Strategies
Alibaba has reiterated its previous advisories that the Fastjson 1.x product line is completely retired and unsupported, reinforcing that users must transition to Fastjson2. Fastjson2 was architecturally redesigned to prevent this class of vulnerability by enforcing a strict allowlist of known safe types before interacting with class loaders, entirely eliminating the remote-fetch primitive from untrusted inputs.

For organizations unable to immediately migrate away from Fastjson 1.x, security engineers recommend the following actionable mitigations:
- Enable Global Safe Mode: Enforcing
-Dfastjson.parser.safeMode=trueforcescheckAutoType()to throw an exception unconditionally at the very beginning of execution, completely blocking the vulnerable code path. However, this will break legitimate applications that rely on polymorphic deserialization via@type. - Adopt Alternative Artifacts: Teams can switch to the
1.2.83_noneautotypebuild, which strips AutoType functionality at compile time, achieving an effect similar to enablingsafeMode. - Strict Egress Filtering: Implementing rigorous outbound network restrictions from production Java Virtual Machines prevents the server from resolving external
jar:http://orjar:https://requests, neutralizing the first stage of the attack chain even if a payload is received. - WAF and Runtime Application Self-Protection (RASP): While Web Application Firewalls (WAFs) attempting to block literal strings like
jar:can be easily bypassed using mixed-case encodings (Jar:) or alternative URI schemes, RASP solutions capable of monitoring internal class-loading behavior offer more robust detection capabilities.
As threat actors begin weaponizing CVE-2026-16723 in the wild, enterprise security teams are strongly advised to audit their dependency trees, identify lingering instances of Fastjson 1.x, and apply network-level controls or migrate to modern, supported libraries immediately.